
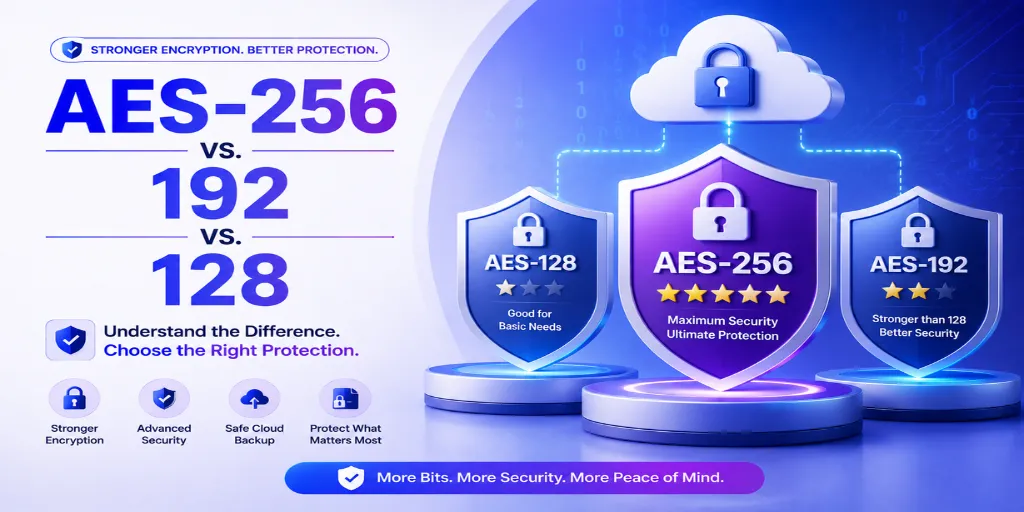
AES-256 vs. 192 vs. 128 — Which Encryption Level Actually Matters for Your Backups
Every backup vendor advertises “military-grade encryption,” but the differences between AES-256, 192, and 128 are widely misunderstood — and mostly irrelevant compared to a much bigger question: who holds the key? Includes a vendor evaluation script you can use today.
“Military-grade encryption” is a phrase worth retiring.
Understanding the signals attackers actually look for is the fastest way to understand what makes your own setup look vulnerable, or not.
“Military-grade encryption” is one of the most overused phrases in backup and security marketing, and it’s almost always attached to AES-256 as if the bit-length alone were the whole security story. It isn’t. This article breaks down what actually differs between AES-256, 192, and 128, why that difference matters far less than most people assume, and what actually determines whether your encrypted backup is genuinely secure.
What AES-256/192/128 actually differ in
The number in each name refers to the encryption key length, which determines the total number of possible keys an attacker attempting a pure brute-force attack would need to try.
Why AES-128 is not meaningfully crackable either
The number of possible keys in AES-128 is large enough that even with extremely optimistic assumptions about future computing power, exhaustive brute-force search remains firmly in the realm of “not practically achievable” for the foreseeable future. This is a widely-shared assessment among cryptographers, not a specific vulnerability disclosure or attack methodology — it’s simply math about key space size.
The real vulnerability: key management, not key length
In practice, encrypted data gets compromised far more often through weak key management — a poorly protected key, a vendor holding a copy of your key, or a compromised credential — than through anyone actually brute-forcing the encryption algorithm itself. This is where the AES-256-vs-128 conversation misses the point: the bit-length debate distracts from the question that actually determines your real-world security.
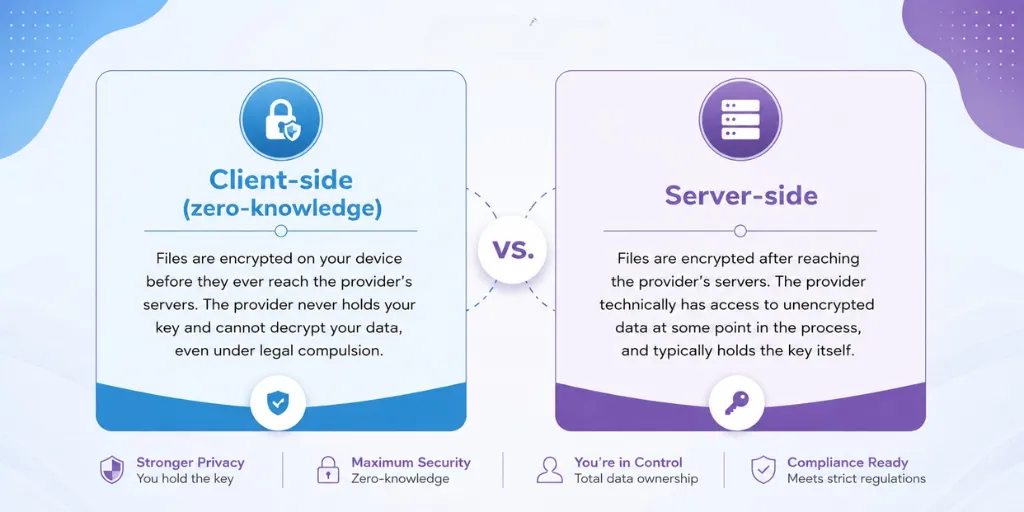
Client-side vs. server-side: where encryption happens
This is the distinction that matters far more than bit-length.
Zero-knowledge encryption, explained plainly
Zero-knowledge means the provider genuinely cannot read your files — not as a policy promise, but as an architectural fact, because they never hold the key needed to decrypt your data. This is a meaningfully stronger security property than bit-length, and it’s worth prioritizing over marketing claims about “256-bit” encryption alone.
Questions to ask any vendor about their actual implementation
Use these three questions, in writing, to evaluate any backup vendor’s real security architecture — not just their marketing page.
Is encryption applied client-side, before data leaves my device?
Do you (the vendor) hold a copy of my encryption key?
In a genuine zero-knowledge architecture, the vendor should not be able to answer “yes” here — if they can decrypt your data on request, your key management isn’t truly zero-knowledge.
What happens to my data if I forget my encryption passphrase?
This is a useful indirect check — a vendor who can simply reset your access to your data without any special recovery process likely holds enough key material to decrypt it themselves.
How Softyz implements this end-to-end
Every Softyz plan uses zero-knowledge encryption applied client-side, before your files ever reach our servers — meaning we genuinely cannot read your data, regardless of bit-length marketing debates. Your key never leaves your control.
Frequently asked questions
Find answers to the most common questions about ransomware protection and backup security.
So AES-128 is genuinely fine, and AES-256 doesn’t matter at all?
What does “zero-knowledge” actually guarantee?
Is server-side encryption inherently bad?
How do I verify a vendor’s zero-knowledge claim, rather than just trusting their marketing page?
The next time a backup vendor leads with “256-bit military-grade encryption” as their headline security claim, the more useful question is the one they didn’t answer: where does encryption actually happen, and who holds the key. That’s where real security lives — or doesn’t.